

This is the first post in a four-part series about a single operation. It is the longest op I have ever worked, and looking back, it is one of the ones that taught me the most about what it actually looks like to do cyber inside a real military exercise. I want to walk through it the way it happened, in order, because the lessons sit better with the context.
A few notes before we start.
I am not going to name the other team that joined us for this op. I am not going to give dates, units, locations beyond what is already public, or any specifics on how we got in. The details have been generalized on purpose. The point of these posts is the experience and the lessons, not the tradecraft. If you are looking for a technical walkthrough, this is not it. If you are looking for what it actually feels like to run a cyber cell during a major Marine Corps exercise, keep reading.
What MWX Is
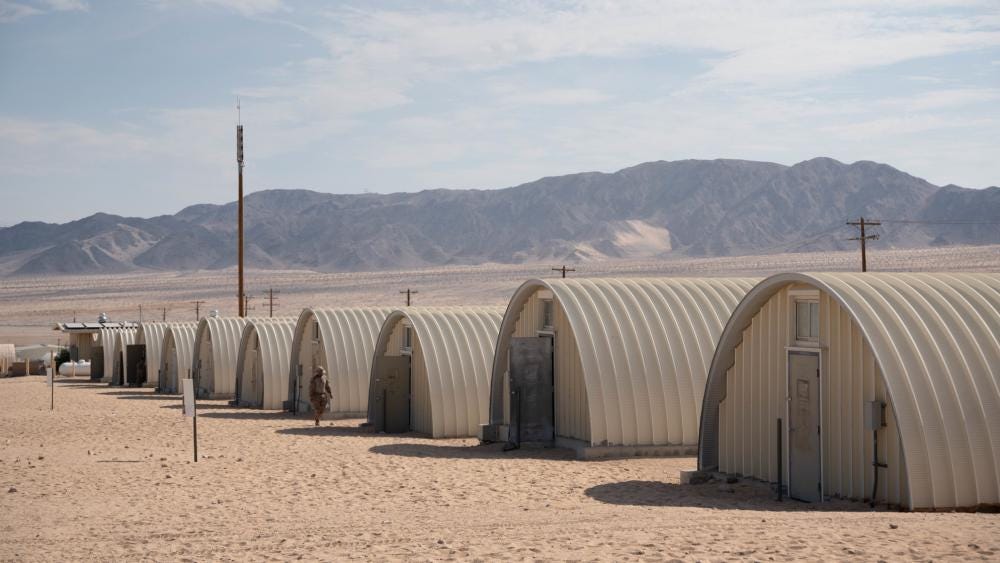
MWX stands for Marine Air Ground Task Force Warfighting Exercise. It is run out of Twentynine Palms, California, in a stretch of desert that is, to put it kindly, an honest place to learn how to fight.
The basic premise is that Marine units go head to head in the desert with capabilities they would almost never get to exercise in a normal training cycle. Special operations, cyber, information operations, influence campaigns, aviation. The full picture of what a modern force actually fights with. These are capabilities that, for most of the units involved, only show up at the high end of real-world operations. MWX gives them a chance to integrate, build the muscle memory, and learn the hard lessons before those lessons get expensive.
For the Marine Corps Red Team, MWX was a different kind of exercise. We were not there to compromise a target for assessment. We were there to act as a real adversary inside a live wargame, working alongside conventional and special operations forces, and providing cyber effects that would have a measurable impact on how the battle unfolded.
If you have never been part of something like this, the simplest way I can describe it is that everything happens at once. The kinetic side is moving. The intelligence side is moving. The cyber side is moving. And the only way it works is if everyone has rehearsed enough to know what their piece of the puzzle is and how it fits into everyone else’s.
We were the cyber cell. I was the lead of that cell for this operation. At the same time, I was the chief of the Marine Corps Red Team, and I was a Gunnery Sergeant. Three hats. All of them mattered.
You can write down what you plan to do, but what actually happens depends on who shows up, what they are carrying, and whether the first punch lands.
The Planning Phase
The planning for this op was, in a word, painful.
Leadership had turned over in the months leading up to MWX, and the new people in the chairs above us did not have a working understanding of cyber. That is not a criticism of them as officers. It is a recognition that cyber is a specialized field, and dropping someone with a different background into the supervisory role over a cyber team without ramp-up time will produce predictable friction. We were in the middle of that friction.
What that friction looked like in practice was a series of long planning calls in the weeks before we headed out to the desert. The new leadership wanted cyber plugged into the Master Scenario Events List, the MSEL, which is the chronologically sequenced outline of simulated events that exercise participants are supposed to respond to during the exercise. It is the backbone of how conventional exercises run. You write down what happens and when, and the exercise unfolds against that timeline.
The expectation was that we would fill in our rows of the MSEL the same way an artillery battery or a logistics section would. Tuesday at 0900, gain initial access. Tuesday at 1100, escalate privileges. Wednesday at 1400, exfiltrate data. Discrete steps with discrete timelines, the same way you would build a schedule for a vehicle convoy or a live-fire range.
That is not how offensive cyber works. It is not how defensive cyber works either, for that matter. Both sides of this game are reactive by nature. You build a plan, but the plan survives contact with reality for about as long as it takes to send the first email. Just like real combat. After that, you are responding to what the target environment is actually doing, what the defenders are noticing, what tools are catching what payloads on what day, and what the network looks like once you are inside it instead of what you assumed it looked like before. The idea that we could write down a sequence of events weeks out and then execute it on schedule was, frankly, not connected to reality.
So we sat on those calls trying to make it work anyway. We built Excel documents full of branching scenarios, guessing at where we might be at various points in the exercise and trying to keep our timelines at least plausible. I was holding back a lot of frustration on those calls. I understood why they wanted the MSEL populated. It is how the rest of the exercise runs. It is how the exercise control element tracks what is happening. But trying to force cyber into that format is like trying to schedule a bar fight. You can write down what you plan to do, but what actually happens depends on who shows up, what they are carrying, and whether the first punch lands.
We pushed back where we could. Some of the pushback worked. Some of it did not.
The Weird Asks
The other thing that came out of that planning cycle was a set of tasking requests that were just strange.
This was not unique to this exercise, and honestly it is not unique to the Marine Corps, military at large, or the private sector for that matter. It is a pattern I have seen across the entire time I have worked in cyber. People who do not have deep experience with the discipline, and sometimes people who do, tend to think of cyber in movie terms. They picture dark rooms and hoodies and someone typing furiously while a progress bar fills up on a screen. They want cyber to be cool. They want the kind of operation that sounds impressive in a briefing, the multi-stage chain that makes the room go “whoa.” What they do not picture is the reality, cyber is a lot of reading code, searching for answers in documentation, and banging your head against a desk until you find something that actually works.
One of the tasking requests that came out of this planning cycle with the unit we were going to work for this time was a multi-stage initial access chain that started with a whaling attack against a specific person’s BlackBerry, pivoted to their Teams account, used that to send a payload to a different person’s phone, and from there moved laterally into the target’s email environment. I am not going to get into whether that chain was technically feasible. The point is that it was wildly more complicated than it needed to be for the access we actually wanted. A normal phishing campaign would have produced the same end state with a fraction of the moving parts. Every step you add to an attack chain is a step that can fail, and the more elaborate the chain, the more places defenders have to spot you.
When you ask why a tasking is built that way, the answer is sometimes that the person writing it has seen something cool in a briefing somewhere and wants to see it happen, regardless of whether it is the right tool for the job. Again, that is not unique to the Marine Corps and it is not unique to cyber. It is just human. But it is the kind of thing you learn to manage, because the people writing the tasking are the people you report to, and you do not get to roll your eyes.
We had a group call about it. I pushed back hard. I told the people on the line that the chain as written was a dumb plan, and I started laying out why. The first stage alone had problems. Whaling is inherently risky because VIPs tend to be closely monitored, which means your phishing attempt is more likely to get flagged before it ever reaches the target. On top of that, the plan assumed the target was carrying a BlackBerry, but the Marine Corps was in the middle of phasing BlackBerries out in favor of iPhones and Androids, so there was no guarantee of what device the person would actually have in their hand on the day. That matters because phone payloads are not computer payloads. The development work, the exploit surface, the delivery mechanism are all different depending on the platform, and building for three possible phones instead of one triples the prep work for a single stage of a chain that had four more stages after it. A normal phishing campaign against a broader target set would have put us in the same position with a fraction of the risk and a fraction of the development time. I was not subtle about it.
Somewhere in the middle of explaining why the plan was bad, it became clear that the officer I was actively talking to was the officer who had written the plan.
I stuck with it. I had already said what I said, and walking it back would have been worse than saying it in the first place. He listened. To his credit, he did get a bit defensive but never combative. He told me, plainly, that he thought it was a cool plan. I told him it was a cool plan. The two statements are not in conflict. A plan can be interesting and also be the wrong plan for the time and resources you have. I walked him through what it would actually take to execute the chain the way he had drawn it up, including the development time, the infrastructure, and the opportunities for the entire op to come apart if any one of the stages did not land. By the end of the conversation he was the one telling me to go with the simpler approach.
Cyber is a lot of reading code, searching for answers in documentation, and banging your head against a desk until you find something that actually works.
I have had many calls like that since. It was not the first time I remember telling something honest to a senior officer who had every reason to take it personally and watching the conversation get better, not worse, because of it. It was though, in retrospect, a piece of foreshadowing for something that happened later in the op with a much more senior officer. We will get to that.
There was another problem hiding in the simple phishing plan, though, which is that the Marine Corps had just stood up a new web proxy capability with remote browser isolation in front of it right before the exercise started. It was kicking our ass. Standard delivery techniques that had worked a quarter ago were getting eaten. We were going to need to build something new before the real op even started.
That realization was a punch in the gut. We had spent weeks preparing, building tooling, testing delivery chains, and a significant chunk of what we had built was suddenly useless against a capability that did not exist the last time we had done this. But that is also part of the game. The target environment does not hold still for you. If it did, the exercise would not be worth running.
That is where Part 2 picks up.
This was a wargame, not an operation. Everything described is notional, generalized, and presented at a level intended to convey the experience and the lessons rather than the tradecraft. No personnel beyond those who have written publicly under their own names are identifiable. No units, dates, locations, techniques, or outcomes are presented in a way that would identify specific systems or people. Where details have been generalized, they have been generalized on purpose.